

What should an intranet be capable of in critical infrastructure

The shift has changed, an operator is in the middle of an incident, and there is a message somewhere on the intranet that the rest of the shift also needs to see immediately. The identity service is acting up, the phone is ringing, and the procedure that should be easy to find is hidden in a structure that only makes sense on a calm day. In critical infrastructure, this is exactly where the difference between a standard intranet and an operationally-driven intranet becomes clear.
This is why the question What should an intranet be capable of in critical infrastructure? is not just about neat communication or nice news pages. It is about whether employees can still access procedures, contact lists, operational messages, and access to work processes when operations are under pressure, and whether the platform is built for strict access control, encryption, segmentation, and controlled recovery as part of the core design, not as an afterthought. In Danish critical infrastructure, the intranet is often the internal channel that binds operations, emergency preparedness, and collaboration together, making the requirements significantly stricter than in a standard office environment.
When the intranet is part of critical operations
A night shift worker at a hospital is looking for an updated isolation procedure, while an operations manager in a utility environment is trying to send an urgent message to multiple locations simultaneously. Both view the intranet as a work tool, not as an internal newspaper. If the page is slow, illogical, or unavailable, the intranet quickly becomes a bottleneck, precisely when it is supposed to help.
In critical infrastructure, this difference is crucial because the intranet must not only inform but also support coordination, secure access, and rapid action. Danish and Nordic guidelines clearly point to access protection, encryption, segmentation, logging, and recovery as fundamental requirements for high-risk, high-consequence environments, as seen in the NCIIPC's guidance and the NSM's basic principles for ICT security.
Practical rule: If an employee cannot find the correct message when under pressure, the intranet is not just a communication problem. It is an operational problem.
A modern intranet for this sector must therefore do more than just publish news. It must be able to handle role-based permissions, display targeted messages to the right employees, and remain useful even when parts of the environment are down. It functions like a fixed notice board in the control room, but with the advantage that content can be managed, tracked, and targeted as needed.
This is also where the boundary with standard internal communication becomes clear. In a sector where access to procedures, contact lists, and operational messages can mean the difference between calm and delay, the intranet must be designed for operations under pressure. For organisations working in utilities and other critical infrastructure, it makes sense to look closer at Colibo for critical infrastructure and utilities as an example of how these requirements can be put into practice.
Six fundamental features that every intranet in critical infrastructure must have
An intranet in critical infrastructure must, first and foremost, be easy to use when people are under pressure. This means that the platform must work across workplaces, shifts, and devices, and that employees must be able to find the most important information without knowing the entire information architecture beforehand.
1. Fast access to the right messages
When an operations manager sends a message about a system outage, it must reach the relevant groups immediately. This is where consistent distribution of operational information becomes more important than classic news dissemination, because operations cannot wait for someone to manually forward information.
2. Role-based access
A nurse, a shift planner, and a technician do not need the same documents or the same editing permissions. Role-based permissions ensure that employees only see what they need, and that sensitive information does not circulate unnecessarily within the organisation.
3. Mobile access on the go
Frontline, operations, and management rarely work in the same place. An intranet must therefore work on mobile devices, so employees can read messages, open procedures, and respond while on the move between locations, in engine rooms, or on shift.
4. Centralised knowledge sharing with search that works
When the intranet consolidates procedures, contact lists, and working documents, the search functionality must be sharp enough to support stressful workdays. AI-assisted search can help find the right content faster, especially when the user does not remember the exact title.
5. Offline or degraded access
If normal operations fail, key information should still be readable in a reduced form. This applies especially to contact lists, key procedures, and operationally critical messages, which must not disappear just because the identity service or a network link is unavailable.
6. Dialogue and follow-up
An intranet in critical infrastructure is not just a noticeboard system. It must also support dialogue, allowing local units to ask questions, confirm receipt, and follow up on incidents without spreading information across too many separate channels.
A good rule of thumb is simple. If the intranet cannot help an employee act quickly during an interrupted workday, it is not built for critical operations. This is also why platforms for this sector should be evaluated on whether they can centralise communication, tools, and access to work processes in one place, without making the user dependent on knowing three other systems first.
Security and compliance as a design principle, not an add-on
An intranet in critical infrastructure quickly becomes a weak point if security is only thought of after the solution has been chosen. The access model, information structure, and publishing process must therefore be shaped together from the beginning, so the platform can be used under pressure without granting overly broad permissions or creating unclear workflows. When operations, emergency response, and incident management are in focus, security must be embedded in the very way the intranet is built.
Encryption and access control as the foundation
Encryption is not just about data in transit, but about making content less vulnerable if something goes wrong. When the intranet handles procedures, incident reports, and sensitive messages, it must be able to tightly control both read and edit access. This is the difference between a locked folder and an open noticeboard.
Role-based control is absolutely key here. It reduces the risk of incorrect permissions granting overly broad access, and it makes it easier to keep track of who is allowed to publish, edit, and approve content. In practice, an operations manager should be able to see what is necessary, while a local editor can only work within their own designated area.
Segmentation and logging in the daily structure
When an intranet is used in critical infrastructure, it should not be one large communal space where everything is mixed together. Operational messages, documents, and HR materials can have different sensitivity levels, and they should therefore reside in separate zones with clear access boundaries. This makes it easier to contain damage if an account or service is compromised.
A good intranet design also incorporates centralised logging of access and changes. This is not just a matter of post-incident audit, but of being able to see who opened, edited, or exported content while it is still relevant to operations. When a control room or an emergency function shares messages, traceability must be as clear as the message itself.
Key point: Logging is not just about knowing who was logged in. It must also show who viewed, modified, or exported content.
Compliance shapes the platform, not just the documentation
ISO 27001, ISAE 3000, and NIS2 are often referred to as compliance, but in critical infrastructure, they also set the direction for how the platform must function in practice. This applies to supplier management, incident detection, response, and recovery, which must be part of the organisation's control environment and the Danish requirements for critical infrastructure NIS2-related requirements in Danish critical infrastructure.
This means that compliance is not something you add on to the solution at the end. It affects how content is approved, how integrations gain access, and how user permissions are reviewed over time. A platform like Colibo security can be evaluated on exactly these types of requirements, as security and access management must be directly visible in the intranet's structure.
Hosting, operations, and data sovereignty in practice
The choice between cloud, Danish or EU hosting, and on-premises depends on how sensitive the organisation's operations are, and how much control is required over data and availability. In some environments, cloud is entirely relevant, while in others, the risk profile demands a more controlled setup. This is particularly visible in environments with strict data sovereignty requirements, where location, access, and the supply chain carry greater weight.
Hosting model | Typically suited for | Requires special attention to |
|---|---|---|
Public cloud | Less sensitive environments and organisations with flexibility | Vendor management, access control, and dependency on external services |
Danish or EU hosting | Organisations with data sovereignty requirements and clearer legal control | Data location, contracts, and recovery procedures |
On-premises | High-security and defence environments, or where internal control is critical | Own operations, backup, patching, and physical security |
What matters is not only where the system is hosted, but who can manage it under pressure. NSM's guidelines on physical security emphasise that critical infrastructure must be quickly restorable in the event of damage, while highly critical infrastructure must be protected against failure and destruction guideline on physical security. This makes redundancy, backup, and restore testing operational issues, not just technical details.
At the same time, NIS2-related requirements point to risk analysis, incident detection, response, recovery, and supplier management as necessary capabilities, meaning that the choice of hosting must support both technical control and documented accountability NSM's guidance on physical security. Therefore, it is realistic to see on-premises as the natural choice in some high-security environments, while Danish or EU hosting often becomes the more practical balance in other public and socio-critical organisations.
How the intranet behaves during an incident
An intranet is only truly tested when something goes wrong. Then, it doesn't help if the platform is only strong in peacetime. It must be able to carry operations forward when identity services are down, the network is unstable, or a cyberattack has altered how employees work.
It is therefore useful to look at three concrete scenarios where normal operations are disrupted, and the platform must still help employees move forward.
The utility company with disconnected access
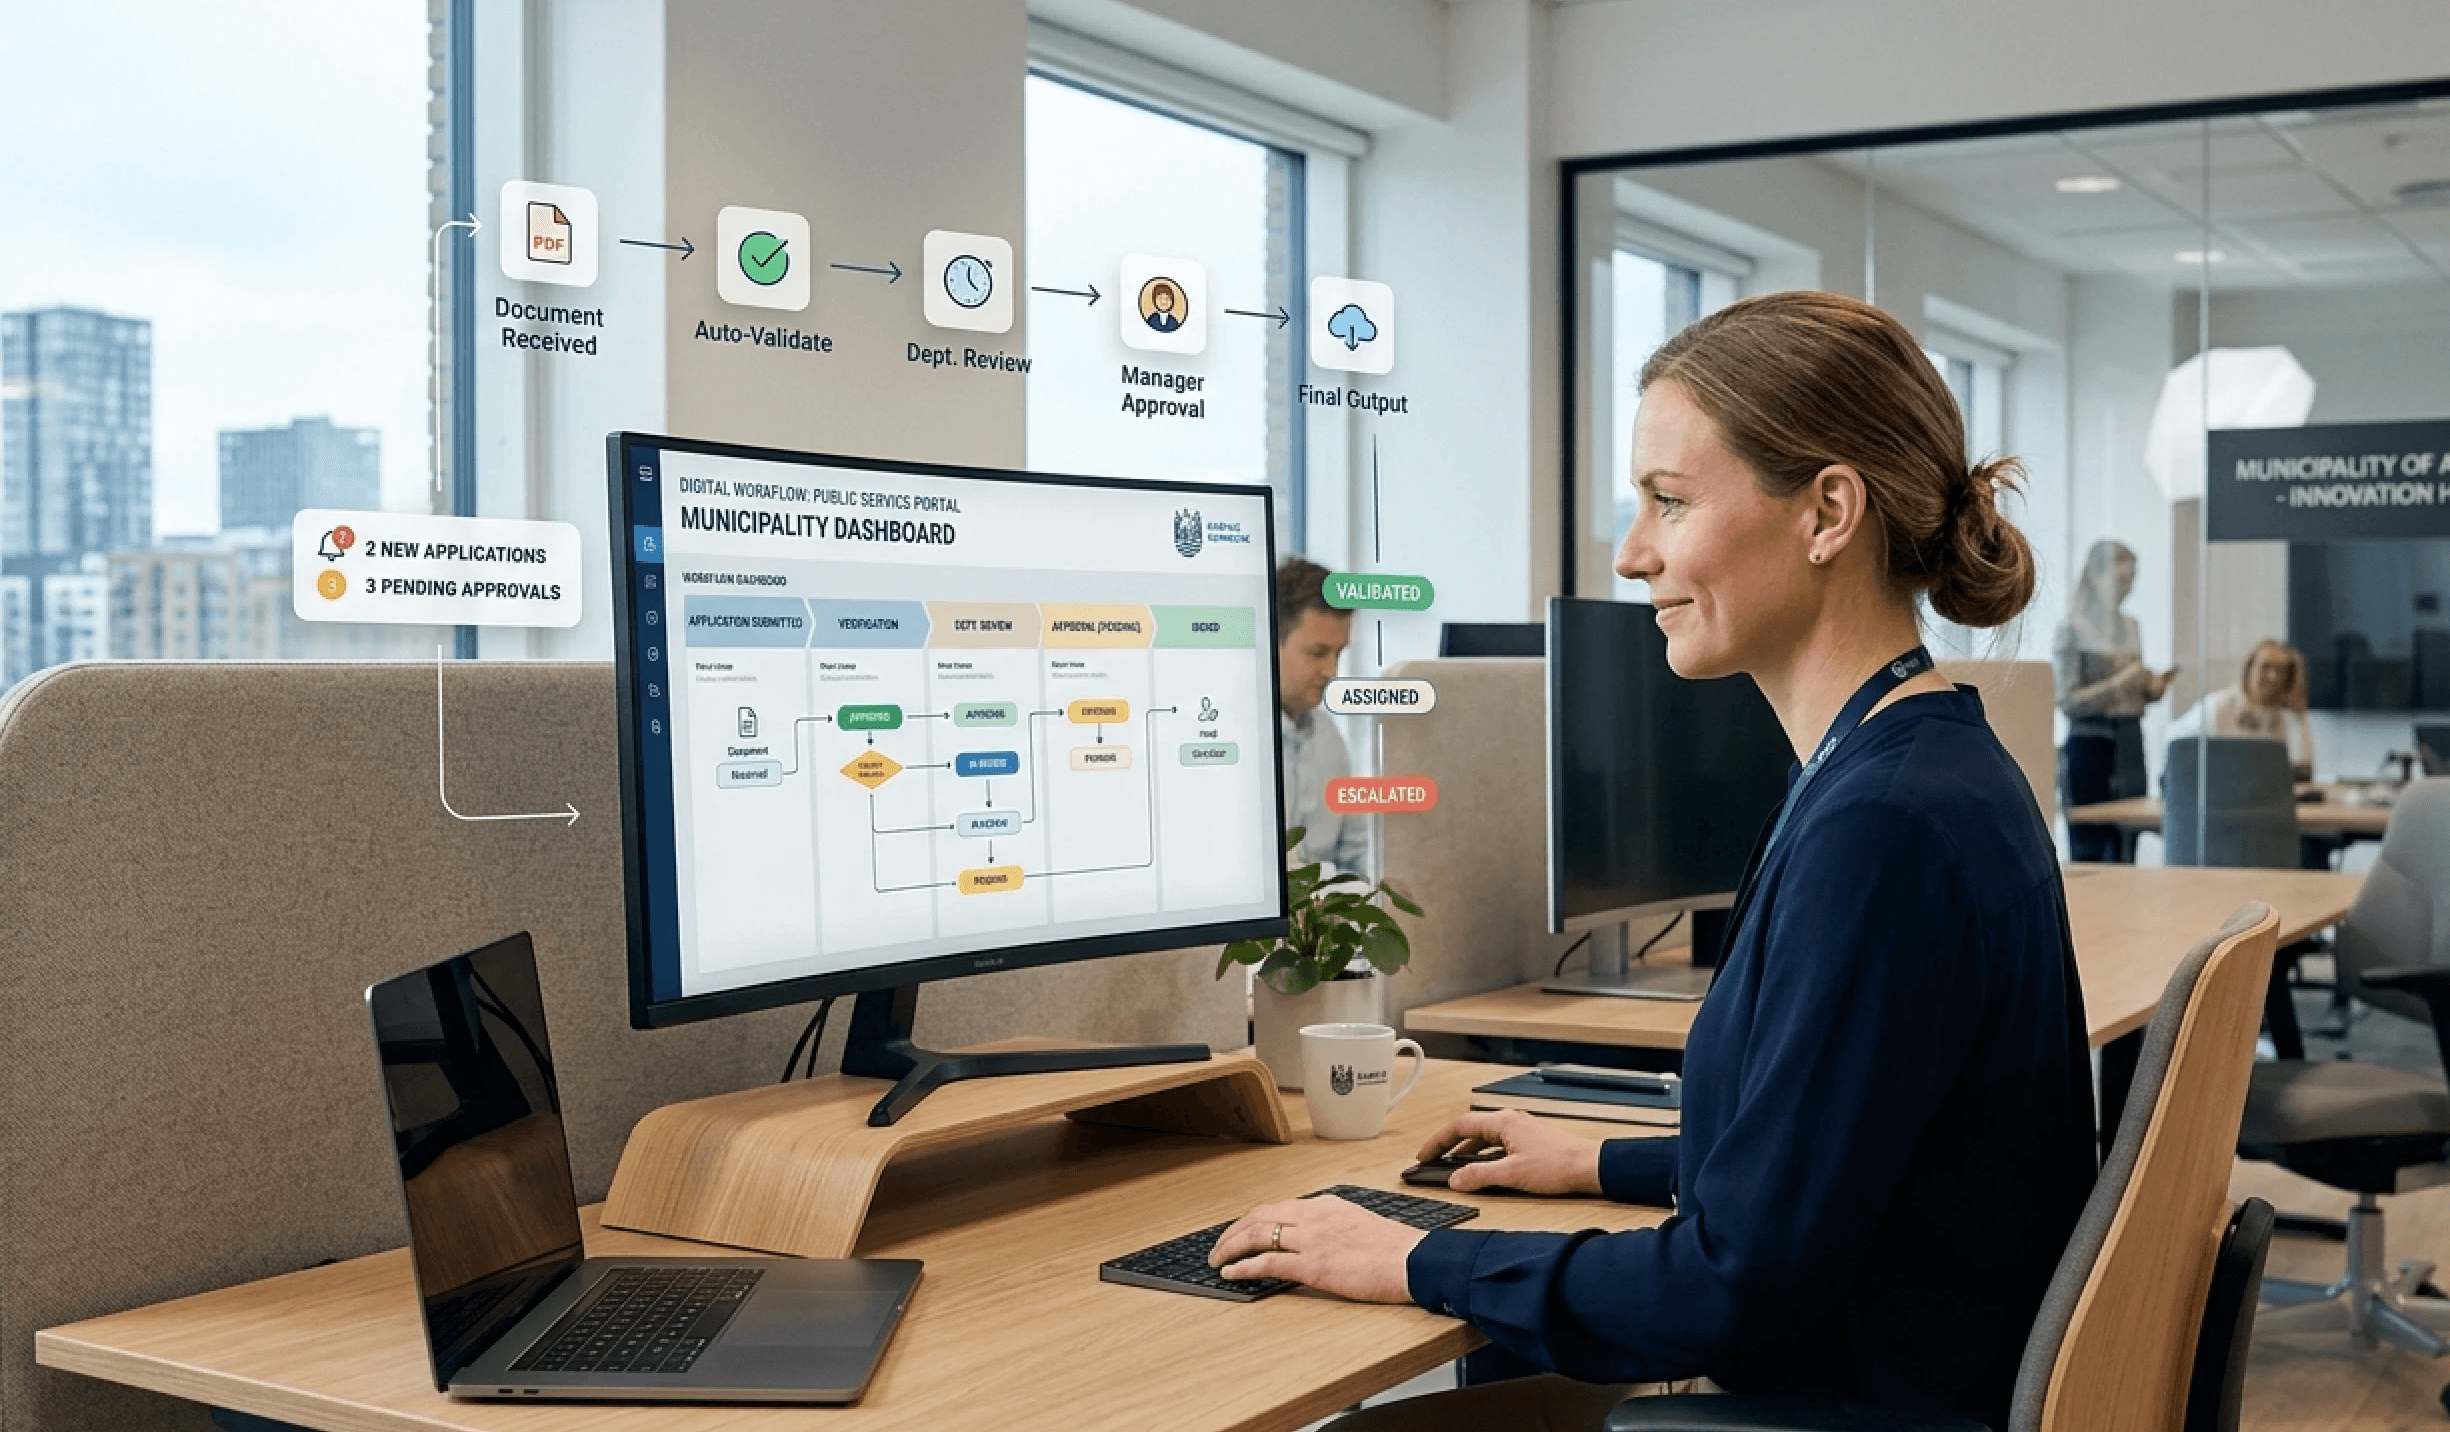
An operations manager needs the latest emergency procedure and the current contact list, but the identity service is unstable. Here, the intranet must be able to display the most critical information in a degraded state, so the employee can still act, even if the full normal user experience is unavailable. This is equivalent to having an emergency folder at hand—not the entire archive, but the pages actually used when decisions must be made quickly.
The hospital during a cyber incident
At a hospital, a department must be notified of changed workflows and temporary restrictions in system usage. The intranet must therefore be able to function as a controlled channel for operational messages, even when other communication channels are under strain, and tight control over who can publish and confirm content is required. Here, it becomes clear that content management is not just about editing, but about who is allowed to say what, when, and with what approval.
An internal emergency response process only adds value if it can be followed in practice. Therefore, it makes sense to link the platform's functions with a clear business continuity approach, so the intranet supports communication, access, and recovery under pressure.
The transport operator with network challenges
A transport operator may need to maintain coordination across shifts and locations, even if parts of the network are down. Here, offline access, mobile notifications, and quick access to procedures become crucial, as the information must be able to reach the frontline, not just the office. This is the difference between a message sitting neatly in the system and a message that actually reaches the team that needs to act now.
The intranet must function as an emergency preparedness platform that keeps operations running even when other systems fail.
It is precisely in these types of situations that sector actors' needs for emergency procedures, isolated operations (island mode), and mapping of network entry points become tangible. Sectorcert's recommendations point to planning for isolated operations and protecting utility-critical IT systems, so that operations can be maintained during extraordinary situations Sectorcert's recommendations.
In practice, this means the intranet must be able to deliver the right messages, even when the organisation's normal comfort layer is gone. Incident response workflows must therefore be clear, so that roles, access, and approval are not improvised in the middle of the incident. It is about making the next step clear for the person tasked with the job, not about adding more features for the sake of features.
Integrations and implementation in a complex IT landscape
A critical intranet rarely needs to replace everything else. Instead, it must connect with what the organisation already uses, without creating double work or extra digital noise. Therefore, implementation should begin with the systems that most employees already interact with in their daily work.
The integrations that typically matter most
Microsoft 365 or Google Workspace: Connection between documents, calendar, and collaboration, so users do not hop between platforms unnecessarily.
Identity services: Consistent access logic makes it easier to manage roles and reduce errors in user administration.
HR systems: Ensures that employee data, teams, and organisational structures are not maintained in duplicate.
Info screens: Makes operational messages visible in common areas, production, and guardrooms.
Specialised systems: Relevant operational tools can be linked in, making the intranet the entry point, not just another stop.
A practical sequence for rollout
First, the organisation should define the pilot group and select the key use cases. After that, governance should be established so that content ownership, permissions, and approvals are clear. Once that works, the platform can be rolled out more widely, and only at the end should more advanced integrations and any platform transitions be fully implemented.
Colibo's platform is relevant to consider in this context because it can be connected to Microsoft 365 and Google Workspace, can be delivered with Danish or EU hosting, and can be operated as a standalone platform or within existing environments. The key is not the name of the platform, but whether it can consolidate information, access, and tools without making the implementation heavier than necessary.
Implementation checklist and how Colibo matches the requirements
A good evaluation basis for critical infrastructure should be brief but sharp. Security and compliance, hosting and data sovereignty, mobile and offline access, integrations, AI-assisted search, as well as emergency response and isolated operations should be at the top, because each of these determines whether the intranet helps when operations are under pressure.
Colibo addresses these requirements with a mobile app, a built-in AI assistant, options for Danish or EU hosting, as well as integrations with Microsoft 365 and Google Workspace. The solution can also run as a standalone platform, making it easier to evaluate in environments where data sovereignty, access control, and controlled operations are heavily weighted.
A practical purchasing test can be phrased like this: Can the platform keep employees updated during incidents, can it control access strictly, can it function across locations and devices, and can it be integrated into the emergency response without creating more complexity than it removes? If the answer is yes, it is relevant for critical infrastructure; if not, it quickly becomes just another system that only works on a good day.
If the organisation needs to select or replace an intranet in an environment with high operational and security requirements, the next step is to see how Colibo can be used as a concrete reference point for requirements regarding mobile access, AI search, Danish or EU hosting, and integrations. Visit Colibo to see how the platform can be included in a serious evaluation of intranets for critical infrastructure.